Yash Kadakia is the Founder and Chief Technology Officer of Security Brigade, and the founder of ShadowMap and B-52, an agentic penetration testing platform.
Press
For comment on a breach, an attack technique or AI in security, write to me. Everything you need to describe me is below.
Biographies
Yash Kadakia is the Founder and Chief Technology Officer of Security Brigade, which he established in 2006 at the age of 19. He also founded ShadowMap, an attack surface and threat intelligence platform, and B-52, an agentic penetration testing platform. His work focuses on how AI is transforming cyberattacks, enterprise risk and security testing.
Yash Kadakia is the Founder and Chief Technology Officer of Security Brigade, which he established in 2006 at the age of 19. With two decades of experience in enterprise cybersecurity, he has built security teams, assessment methodologies and technology platforms serving major financial institutions and enterprises. He is also the founder of ShadowMap, an attack surface and threat intelligence platform, and B-52, an agentic penetration testing platform. His work focuses on how AI is transforming cyberattacks, enterprise risk and security testing. His commentary and the work of his companies have featured in Financial Times, POLITICO Europe, Forbes India, The Economic Times and CSO Online.
Yash Kadakia is the Founder and Chief Technology Officer of Security Brigade, a cybersecurity firm he established in 2006 at the age of 19. Over two decades, he has built security teams, assessment methodologies and proprietary platforms to help organisations understand their exposure and strengthen their defences.
His experience spans enterprise cybersecurity, application security, penetration testing and red teaming. At Security Brigade, he built the business around detailed, expert-led assessments that examine how systems operate, how controls fail and how individual weaknesses combine into larger attacks.
Alongside the security practice, Yash developed Lemon, the company’s internal assessment platform, to capture testing knowledge, enforce workflows and maintain consistent quality as the team grew. That focus on combining expert judgement with technology continues through ShadowMap and B-52.
He founded ShadowMap to help organisations discover their external attack surface and connect threats across exposed infrastructure, leaked credentials, dark-web activity and brand impersonation. He is also the founder of B-52, an agentic penetration testing platform that applies AI to assessment planning, application analysis, exploitation and evidence-based reporting.
His current work spans using AI to conduct security assessments and evaluating the risks introduced by AI applications and autonomous agents. He brings a practitioner’s perspective to cybersecurity strategy, emerging threats and their implications for enterprise leadership and oversight.
Yash has spoken at industry forums including the NASSCOM-DSCI Annual Information Security Summit and Nullcon. His commentary and the work of his companies have featured in Financial Times, POLITICO Europe, Forbes India, The Economic Times and CSO Online.
Yash Kadakia is the Founder and CTO of Security Brigade, which he started at 19 and has led for two decades. He is also the founder of ShadowMap and B-52, an agentic penetration testing platform. His work combines enterprise security experience with AI-driven technology, bringing a practical perspective to how organisations can keep pace with evolving cyber threats.
Photos
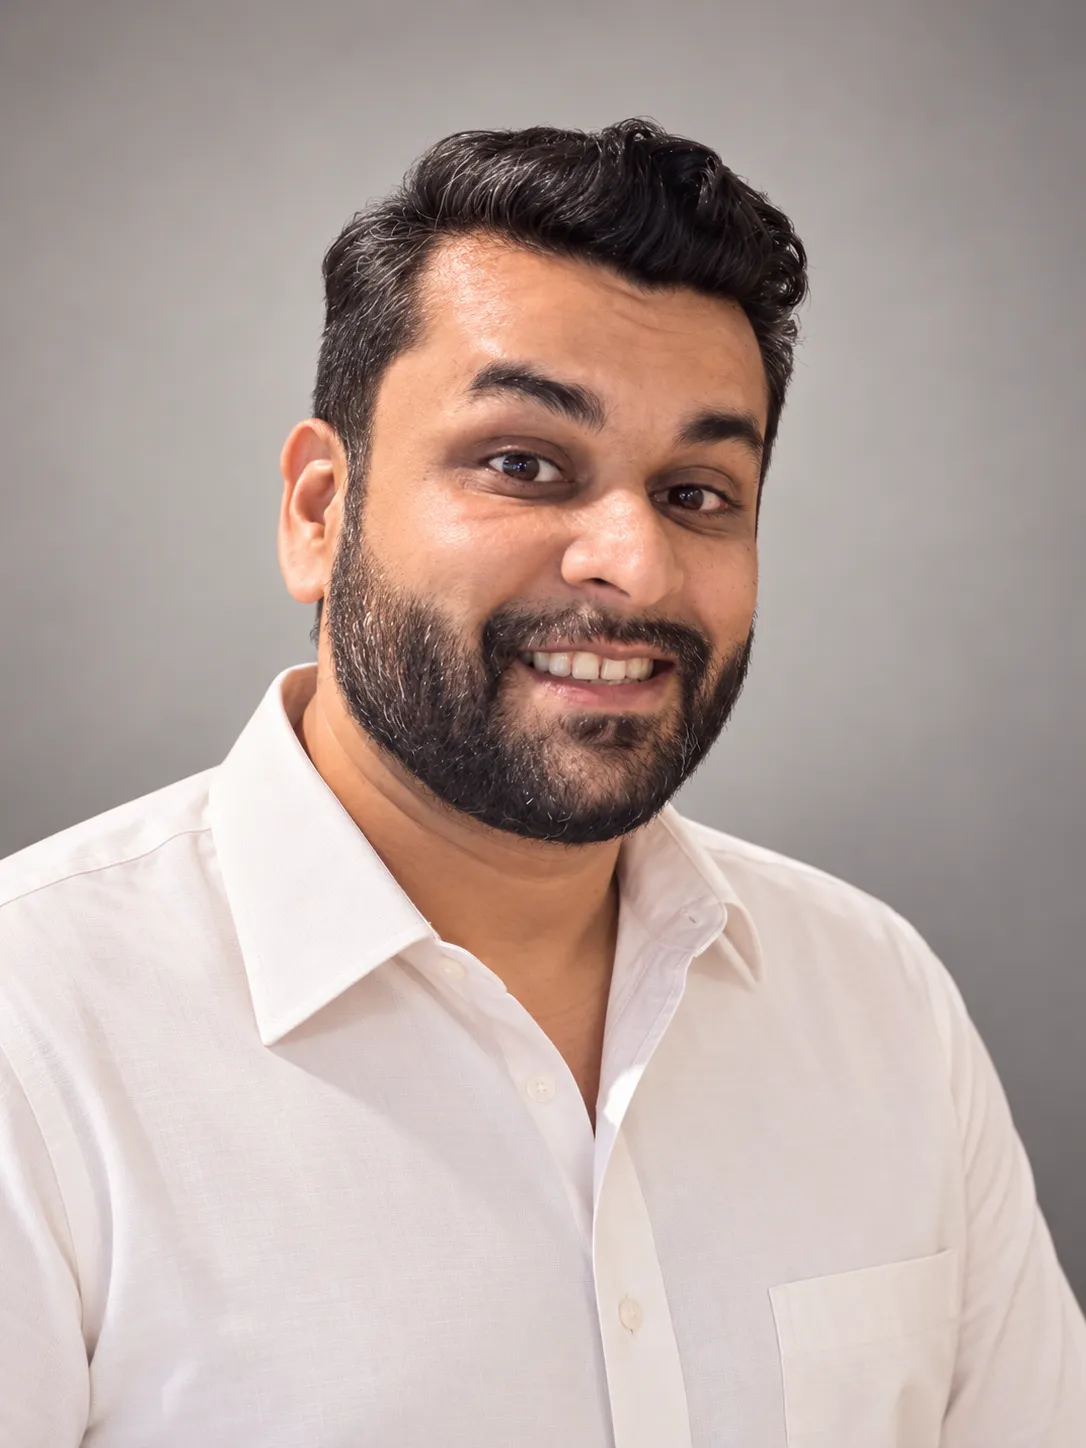
Download PNG
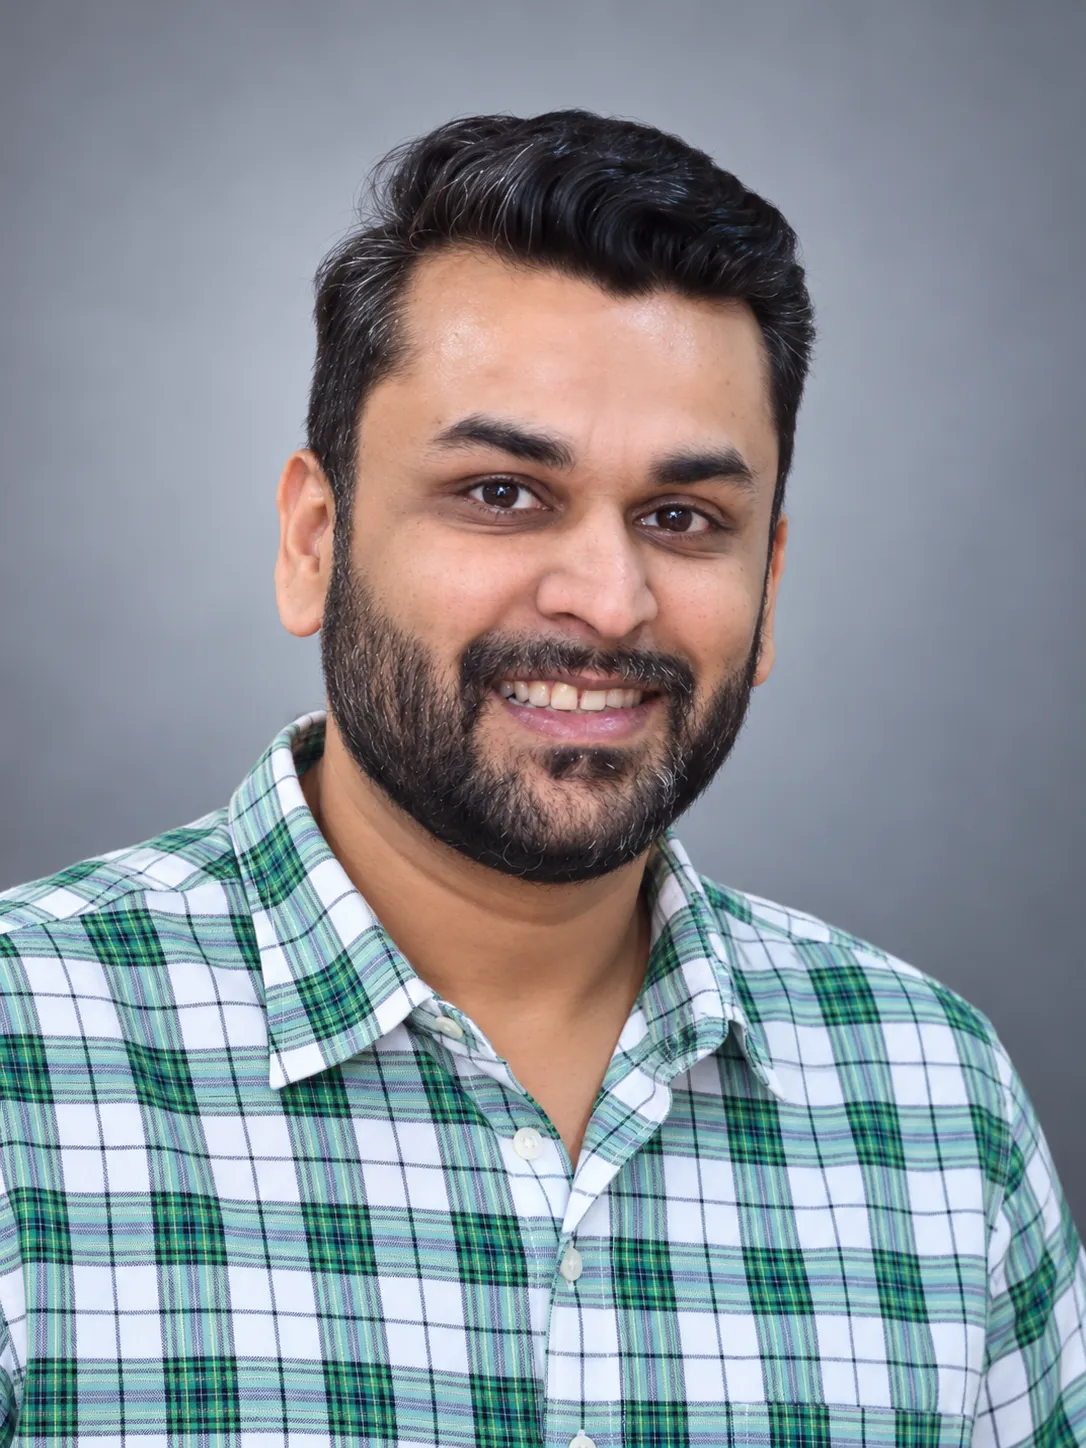
Download PNG
Fact sheet
- Name
- Yash Kadakia
- Role
- Founder and CTO of Security Brigade, the company behind ShadowMap and B-52
- Based in
- Mumbai, India
- Founded Security Brigade
- 2006, in Mumbai, at the age of 19
- Scale
- 6,700+ security assessments for 1,000+ clients across banking, insurance, fintech, manufacturing, healthcare and technology. 150+ specialists
- Regulatory work
- CERT-In, RBI and SEBI assessments
- Company credentials
- Security Brigade: CERT-In empanelled since 2008, ISO/IEC 27001 certified. ShadowMap: DSCI Excellence Award 2017, Most Innovative Product of the Year.
- ShadowMap
- External attack surface and threat intelligence platform. Launched 2016. 150+ enterprises.
- B-52
- Agentic penetration testing platform. Completed all 104 XBOW validation challenges without runtime steering, November 2026.
- Offices
- Mumbai, London, New York, Singapore
- Subjects
- AI-driven attacks, AI in security testing, the risks of AI applications and agents, banking and fintech security in India
- Security Brigade has worked with
- ICICI Bank, HDFC Bank, Reserve Bank of India, NPCI, PhonePe, Amazon Pay, Mahindra, Infosys, Etihad Airways
Subjects I comment on
- AI-driven attacks and the economics of cybercrimeAI makes it cheaper to attack one more organisation, and that changes which targets are worth an attacker’s time.
- Banking, fintech and payment security in IndiaAttackers increasingly reach banks through fintech integrations, NBFCs, vendors, exposed APIs and compromised credentials.
- Logins, transactions and fraud on financial platformsA successful login is not an authorised transaction. Checks on money movement have to happen after sign-in.
- Third-party and supply-chain riskA supplier account, partner integration or IDE extension that can reach customers, money or code is part of the attack surface.
- Attack surface and exposed credentialsWhat matters is where a weakness leads, not how it scores on its own.
- AI agents and what they may accessBusinesses deploying AI agents need to settle what those agents can access, what they can decide and what they may execute.
- Breach response and what a fix provesA fix being applied and a check for past access are different things. An available patch is not a protected system.
- Certificates, audits and assuranceThe eMudhra key compromise: which systems still trust the affected authority, and what to ask a certificate authority.
Coverage
- 17 Nov 2026El Ecosistema StartupQwen4-Max: Alibaba baja 62% el costo por tarea de IA ↗Quoted
- 16 Nov 2026Quoted
- 14 Nov 2026Fortune IndiaBanks’ data breaches: India in constant state of digital pandemic; new vaccine needed regularly, say experts ↗Quoted
- 6 Nov 2026Quoted
- 5 Nov 2026Quoted
- 5 Nov 2026The Economic Times, The Morning BriefIndia’s Banks Under Cyberattack: How AI Is Changing the Game ↗Podcast
- 5 Nov 2026Quoted
- 2 Nov 2026Quoted
- 2 Nov 2026Quoted
- 28 Oct 2026Computerworld EspañaLas aplicaciones falsas de ChatGPT y Claude difunden “malware” a través de archivos binarios de IA firmados ↗Quoted
- 28 Oct 2026Quoted
- 23 Oct 2026Quoted
- 23 Oct 2026Quoted
- 23 Oct 2026Quoted
- 23 Oct 2026Quoted
- 22 Oct 2026Quoted
- 22 Oct 2026Quoted
- 22 Oct 2026Quoted
- 22 Oct 2026Quoted
- 21 Oct 2026Hindustan TimesCentre orders probe as Bengaluru firm eMudhra’s key-making error leaves holes in web security ↗Quoted
- 21 Oct 2026BusinessLineeMudhra’s flawed certificate triggers CERT-In probe and raises questions on digital trust ↗Quoted
- 21 Oct 2026Quoted
- 21 Oct 2026Quoted
- 21 Oct 2026Quoted
- 21 Oct 2026Quoted
- 21 Oct 2026Quoted
- 20 Oct 2026BankInfoSecurityWeak Certificates From Indian CA Cause Cascade of Updates ↗Quoted
- 20 Oct 2026The Indian ExpressRogue AI agents target Indian systems: What CERT-In found, why experts are worried ↗Quoted
- 27 Jul 2026Fortune IndiaBank of Baroda confirms data breach; cybersecurity experts see 1TB breach as ‘bad’ and ‘concerning’ ↗Quoted
- 5 May 2026Quoted
- 24 Apr 2026Forbes IndiaWhy India is scrambling over Claude Mythos ↗Quoted
- 8 Apr 2024Quoted
- 8 Apr 2024The Times of IndiaName, address, contact number, email ID and other details of 7.5 million Boat customers leaked on Dark Web, claims report ↗Quoted
- 21 Feb 2021Hindustan TimesEx-defence personnel hit by phishing attack ↗Company research cited
- 16 May 2020Company research cited
- 11 Mar 2020MediaNama‘Data localisation won’t help with cyber security,’ say cyber security professionals, researchers ↗Quoted
- 8 Nov 2019The Economic TimesISRO warned of a possible cyberattack when Dtrack came calling ↗Company research cited
- 7 Nov 2019Financial TimesSuspected North Korea hackers targeted Indian space agency ↗Company research cited
- 8 Apr 2018The Times of IndiaBSF website down, malware sending fake e-mails detected ↗Quoted
- 30 Jan 2012Business StandardWanted: Ethical hackers ↗Quoted
- 25 Oct 2010Business StandardThe rise and rise of cyber security professionals ↗Quoted